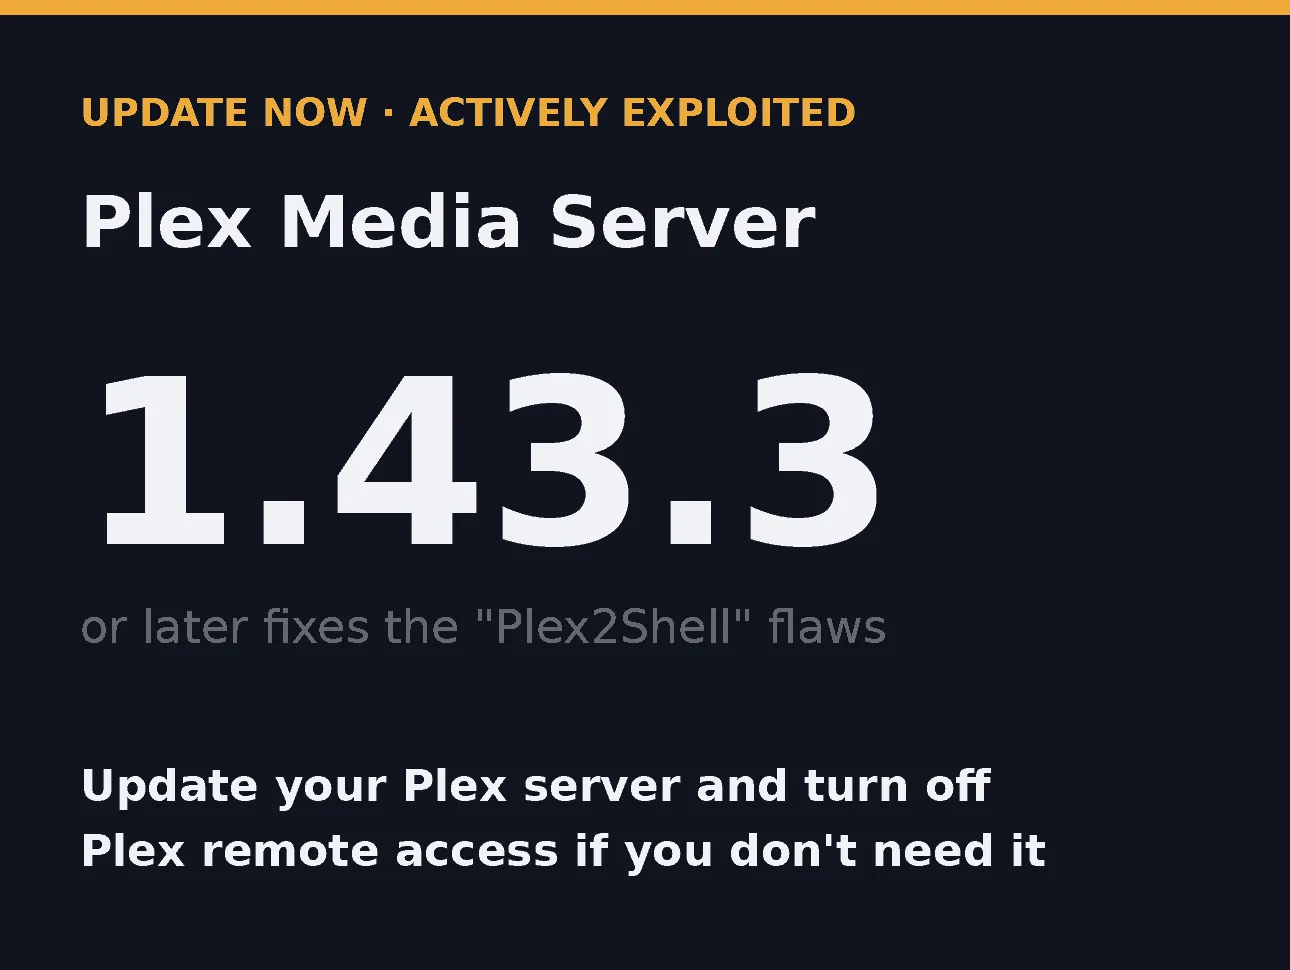
- Plex has confirmed the four Plex2Shell flaws are being actively and widely exploited. A public proof of concept appeared on October 16. Attackers have used compromised servers for cryptocurrency mining and proxy software. QNAP says some of its NAS users have reported compromised Plex servers.
- Anyone running Plex Media Server 1.43.2 or earlier, on a PC, Mac or NAS. The highest risk is a server reachable from the internet, for example through Plex Remote Access, a forwarded port 32400 or UPnP. QNAP says its own QTS and QuTS hero systems are not themselves vulnerable.
- Update Plex Media Server, then confirm the version in Plex Web under Settings, General. If you don't need remote access, turn off Remote Access and stop forwarding port 32400; if you do, QNAP suggests using a VPN instead.
- If your server was reachable from the internet on an older version, QNAP says to treat the device as possibly compromised: check for signs of compromise, do a clean reinstall where needed, and reset your Plex and device passwords.
Useful?