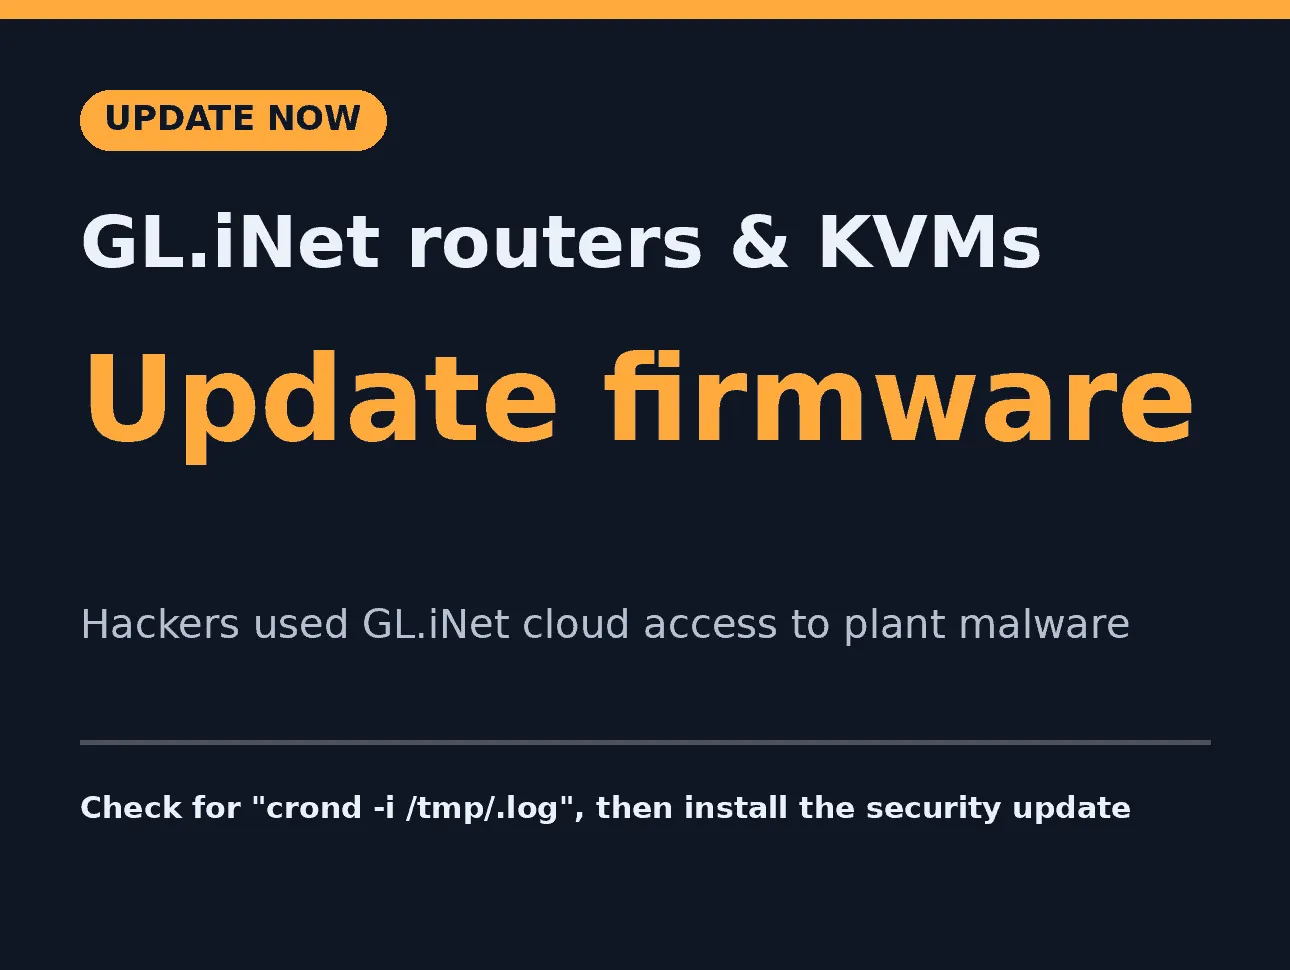
- GL.iNet found the flaw on November 20, 2026, and says it was actively exploited.
- Attackers installed malicious software on some routers and KVM devices.
- The cloud flaw is fixed and the access path blocked, but existing infections remain until cleaned.
- No device count has been given.
- Routers: in LuCI under Status > Processes, or over SSH with: ps | grep tmp
- KVMs: in the web interface, Toolbox > Terminal; run ps -a | grep tmp on the RMQ1, or ps -aux | grep tmp on other models.
- If unsure, GL.iNet asks you to contact its support.
- Stable security firmware for routers and KVMs was scheduled for November 22, 2026.
- KVM beta fixes are out now: 1.10.2 beta or later for RM10, RM10RC, RM1, RM1V2, RM1PE and RM4PE; 1.8.6 beta or later for RMQ1.
- An infected KVM can also be factory reset, which erases its settings.
- Look for unfamiliar programs, browser extensions, user accounts, startup items, scheduled tasks and unusual network activity on the connected computer, and run a full security scan.
Useful?